Close Menu
InfovistarInfovistar
  • AI & ML
  • Cybersecurity
  • Money
    • Personal Finance
  • Insights
    • Tech News
    • Tech Tips
    • Startup
    • Web Development
    • AWS and Cloud
    • Technology
  • Courses
    • Machine Learning
      • Python Tutorial
      • TensorFlow Tutorial
      • OpenCV
    • DSA
      • Data Structures
    • Web Development
      • PHP Tutorial
      • CodeIgniter Tutorial
      • CodeIgniter 4 Tutorial
      • CodeIgniter 4 AJAX
      • JavaScript
    • Mobile App Development
      • Android Tutorial
  • Tools
    • Beautifier
      • HTML Beautifier
      • JavaScript Beautifier
      • CSS Beautifier
    • Online Compilers
      • Python Compiler
      • Java Compiler
      • JavaScript Editor
      • PHP Compiler
      • C++ Compiler
      • C Compiler
    • Image Optimization
      • Image Compressor
      • JPEG to PNG
      • PNG to JPEG
      • WebP to PNG
Trending News
Best DDoS Protection Services

10 Best DDoS Protection Services for 2027

November 5, 2026
Best Web Application Firewalls

12 Best Web Application Firewalls (WAF) for 2027

November 4, 2026
Best Ethical Hacking Tools

Best Ethical Hacking Tools in 2027: Free & Paid Picks

November 3, 2026
Facebook X (Twitter) Instagram
Friday, November 6
Trending
  • 10 Best DDoS Protection Services for 2027
  • 12 Best Web Application Firewalls (WAF) for 2027
  • Best Ethical Hacking Tools in 2027: Free & Paid Picks
  • Software supply chain attacks 2026: Timeline and developer checklist
  • Binance Hack: $6.3 Billion Drained in the Largest Crypto Theft Ever. What We Know So Far
  • This Site Uses XSLT Chrome Warning Explained: How to Fix It
  • iPad mini OLED Price in India: Wi-Fi & Cellular Variants, Offers
  • iMac M6 Price in India: All Variants, Colors, Offers and Release Date
Facebook X (Twitter) Instagram Pinterest LinkedIn WhatsApp
InfovistarInfovistar
  • AI & ML
  • Cybersecurity
  • Money
    • Personal Finance
  • Insights
    • Tech News
    • Tech Tips
    • Startup
    • Web Development
    • AWS and Cloud
    • Technology
  • Courses
    • Machine Learning
      • Python Tutorial
      • TensorFlow Tutorial
      • OpenCV
    • DSA
      • Data Structures
    • Web Development
      • PHP Tutorial
      • CodeIgniter Tutorial
      • CodeIgniter 4 Tutorial
      • CodeIgniter 4 AJAX
      • JavaScript
    • Mobile App Development
      • Android Tutorial
  • Tools
    • Beautifier
      • HTML Beautifier
      • JavaScript Beautifier
      • CSS Beautifier
    • Online Compilers
      • Python Compiler
      • Java Compiler
      • JavaScript Editor
      • PHP Compiler
      • C++ Compiler
      • C Compiler
    • Image Optimization
      • Image Compressor
      • JPEG to PNG
      • PNG to JPEG
      • WebP to PNG
InfovistarInfovistar
Home » HTTP/2 DoS attack can crash web servers with a single connection
Cybersecurity

HTTP/2 DoS attack can crash web servers with a single connection

InfovistarBy InfovistarApril 5, 2024Updated:June 1, 20245 Mins Read
Share Facebook Twitter Pinterest LinkedIn Tumblr Reddit Telegram Email
HTTP2 DoS attack can crash web servers with a single connection
Share
Facebook Twitter LinkedIn Pinterest Email

A new vulnerability in the HTTP/2 protocol, called “CONTINUATION Flood,” (DoS) can lead to denial of service (DoS) attacks and potentially crash your server with just a single connection from an attacker.

HTTP/2, introduced as an update to the HTTP protocol in 2015, was designed to enhance web performance significantly. It achieved this by introducing several key features, including binary framing for efficient data transmission, multiplexing to enable multiple requests and responses over a single connection, and header compression to reduce overhead.

How Does It Work?

Recent research by Barket Nowotarski has shed light on critical flaws within the HTTP/2 protocol. Nowotarski’s findings indicate that these vulnerabilities stem from the improper handling of HTTP/2 CONTINUATION frames in many implementations of the protocol.

To understand the issue, it’s essential to grasp how HTTP/2 messages are structured. Furthermore, these messages consist of header and trailer sections serialized into blocks. Additionally, these blocks can be fragmented across multiple frames for transmission, with CONTINUATION frames being utilized to stitch the stream together.

The oversight in many implementations lies in the lack of proper frame checks. This allows malicious actors to exploit the protocol by sending an excessively long string of frames without setting the ‘END_HEADERS’ flag. Consequently, servers may experience out-of-memory crashes or CPU resource exhaustion as they attempt to process these frames.
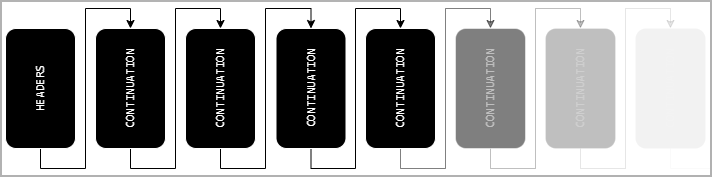
The endless stream of CONTINUATION frames causing DoS (nowotarski.info)

Of particular concern is the risk of out-of-memory conditions, which can result in server crashes using a single HTTP/2 TCP connection in certain implementations. Nowotarski emphasizes the severity of this issue, highlighting that affected implementations fail to limit the size of header lists built using CONTINUATION frames.

Vulnerabilities and Exposures (CVE) IDs

Several Common Vulnerabilities and Exposures (CVE) IDs have been assigned to different HTTP/2 implementations vulnerable to these attacks. These vulnerabilities range from memory leaks and consumption to CPU exhaustion, impacting a variety of platforms and services, including Node.js, Envoy, Tempesta FW, amphp/http, Go, Apache httpd, and Apache Traffic Server.

  • CVE-2024-27983: Affects Node.js HTTP/2 server. Sending a few HTTP/2 frames can cause a memory leak due to a race condition, leading to a potential DoS.
  • CVE-2024-27919: Affects Envoy’s oghttp codec. Unlimited memory consumption due to not resetting a request when header map limits are exceeded.
  • CVE-2024-2758: Relates to Tempesta FW. Its rate limits are not effectively preventing empty CONTINUATION frame attacks, potentially allowing DoS.
  • CVE-2024-2653: Affects amphp/http. It collects CONTINUATION frames in an unbounded buffer, risking an OOM crash if the header size limit is exceeded.
  • CVE-2023-45288: Affects Go’s net/http and net/http2 packages. Allows an attacker to send an arbitrarily large set of headers, causing excessive CPU consumption.
  • CVE-2024-28182: Involves an implementation using the nghttp2 library, which continues to receive CONTINUATION frames, leading to a DoS without proper stream reset callback.
  • CVE-2024-27316: Affects Apache Httpd. A continuous stream of CONTINUATION frames without the END_HEADERS flag set can be sent, improperly terminating requests.
  • CVE-2024-31309: Affects Apache Traffic Server. HTTP/2 CONTINUATION A DoS attack can cause excessive resource consumption on the server.
  • CVE-2024-30255: Affects Envoy versions 1.29.2 or earlier. Vulnerable to CPU exhaustion due to a flood of CONTINUATION frames, consuming significant server resources.

Severe impact

The gravity of the situation is underscored by the confirmation from vendors and HTTP/2 libraries, including Red Hat, SUSE Linux, Arista Networks, and others, that they are impacted by at least one of the identified CVEs. With HTTP traffic constituting a significant portion of all internet transfers, the widespread nature of these vulnerabilities demands urgent attention.
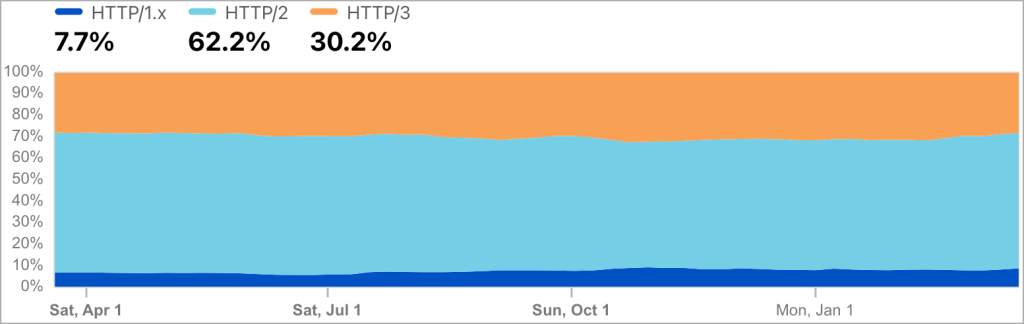
HTTP/2 adoption in the last 12 months (Cloudflare)

Nowotarski warns that addressing these vulnerabilities may prove challenging for server administrators, particularly without adequate HTTP/2 knowledge. Malicious requests exploiting these vulnerabilities may not be readily detectable in access logs, complicating mitigation efforts.

Protecting Your Web Server

Here’s what you can do to mitigate the risk:

  • Patch Early, Patch Often: This is the golden rule of security. Check with your software vendors for updates that address these vulnerabilities. Updating your HTTP/2 libraries and server software is critical.
  • Stay Informed: Subscribe to security advisories from CERT/CC or reputable security news sources. This will keep you updated on the latest threats and available patches.
  • Consider Additional Security: While patching is essential, consider implementing extra security measures. Web application firewalls (WAFs) can add another layer of defense by filtering out malicious traffic before it reaches your server.

As threat actors continue to exploit newly discovered DDoS techniques, timely upgrades to impacted servers and libraries are imperative. Failure to address these vulnerabilities promptly could expose servers to exploitation, posing significant risks to online services and users alike.

Related Articles:
  • 2M+ WordPress Sites Hit By Essential Addons For Elementor Vulnerability
  • New Loop DoS Attack Targets Hundreds of Thousands of Systems
  • Infosys Ransomware Attack: A Wake-Up Call for the IT Services Sector
  • Top Skills Required to Start Your Career in Cybersecurity
Share. Facebook Twitter Pinterest LinkedIn Tumblr Email
Previous ArticleTop 5 ‘Hidden’ Features of Gmail You Must Know
Next Article 20 Best AI Tools For Business in 2024
Infovistar
  • Website
  • Facebook
  • X (Twitter)
  • Instagram
  • LinkedIn

Related Posts

Best DDoS Protection Services
Cybersecurity

10 Best DDoS Protection Services for 2027

November 5, 2026
Best Web Application Firewalls
Cybersecurity

12 Best Web Application Firewalls (WAF) for 2027

November 4, 2026
Best Ethical Hacking Tools
Cybersecurity

Best Ethical Hacking Tools in 2027: Free & Paid Picks

November 3, 2026
Add A Comment

Comments are closed.

Blog Categories
  • AI and ML (106)
  • Android (4)
  • AWS and Cloud (9)
  • Cybersecurity (81)
  • Money (12)
  • Personal Finance (6)
  • Startup (37)
  • Tech News (82)
  • Tech Tips (28)
  • Technology (73)
  • Web Development (25)
Top Posts
Google is rolling out Identity Check Feature to Android 15

Google is rolling out Identity Check Feature to Android 15

January 25, 20252,375 Views
How to Integrate Google Gemini to WhatsApp

How to Use Google Gemini with WhatsApp in 2026

February 16, 20241,913 Views
OpenAI Unveils Web-Based AI Agent Operator for Task Automation

OpenAI Unveils Web-Based AI Agent Operator for Task Automation

January 24, 20251,507 Views
Stay In Touch
  • Facebook
  • YouTube
  • WhatsApp
  • Twitter
  • Instagram
  • Pinterest
  • LinkedIn
Latest Articles

Subscribe to Updates

Get the latest tech news from FooBar about tech, design and biz.

About Us

Infovistar is a technology blog offering practical tutorials, programming guides, and the latest updates on AI, cybersecurity, software development, and digital technology.

Contact Information

Address: Nashik, Maharashtra, India – 422004
Email: infovistarindia@gmail.com
Phone: +91 89990 59150

Contact Us | About Us

DMCA.com Protection Status
Most Popular
Best DDoS Protection Services

10 Best DDoS Protection Services for 2027

Best Web Application Firewalls

12 Best Web Application Firewalls (WAF) for 2027

Best Ethical Hacking Tools

Best Ethical Hacking Tools in 2027: Free & Paid Picks

Our Picks
Binance Hack: $6.3 Billion Stolen, Largest Crypto Heist Ever

This Site Uses XSLT Chrome Warning Explained: How to Fix It

iPad mini OLED Price in India

iPad mini OLED Price in India: Wi-Fi & Cellular Variants, Offers

iMac M6 Price in India

iMac M6 Price in India: All Variants, Colors, Offers and Release Date

Facebook X (Twitter) Instagram Pinterest YouTube LinkedIn
  • About Us
  • Contact Us
  • Tools
  • Terms & Conditions
  • Privacy Policy
  • AdSense Disclaimer
© 2026 Infovistar. Designed and Developed by Infovistar.

Type above and press Enter to search. Press Esc to cancel.

Ad Blocker Enabled!
Ad Blocker Enabled!
Our website is made possible by displaying online advertisements to our visitors. Please support us by disabling your Ad Blocker.